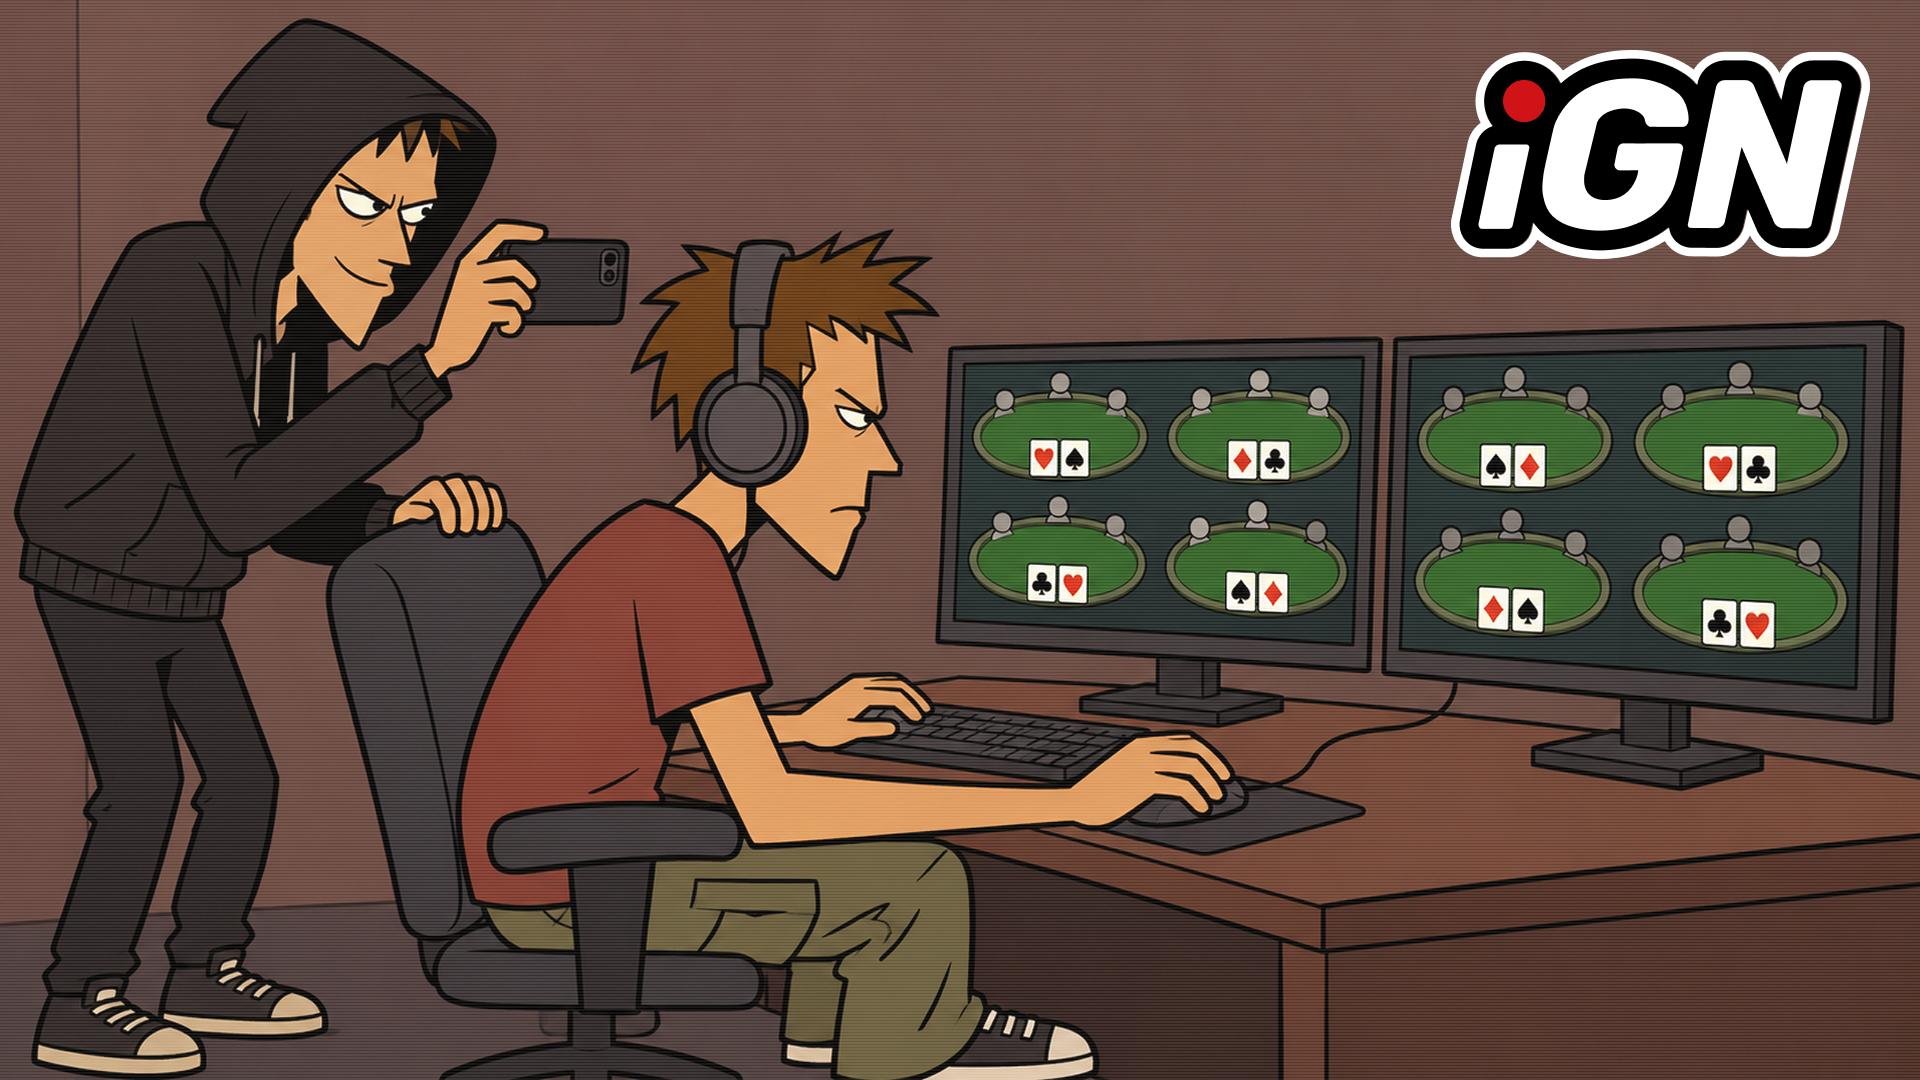
Several leading online poker platforms, including GGPoker, Americas Cardroom (ACR), CoinPoker, and ClubWPT Gold, have been targeted by a sophisticated malware scheme that allowed a hacker to view players’ hole cards for nearly two years. The breach, which began in early 2025 and continued until September 2026, was uncovered after an AI agent detected suspicious activity on a professional player’s computer.
Malware Delivered via Popular Multi-Tabling Tools
The attacker exploited updates to two widely used third-party programs, Jurojin and IntuitiveTables, which help players manage multiple poker tables simultaneously. By compromising the update channels of these applications, the hacker distributed malicious code to hundreds of players. The malware specifically targeted a list of high-stakes players, installing the remote-access tool MeshAgent on their computers if their usernames matched the attacker’s predetermined list.
Impact on Players and Operators
The scheme allowed the perpetrator to covertly observe the cards of targeted players during live games, giving them a decisive advantage. The estimated financial losses range from $1.5 million to $4 million, affecting hundreds of accounts. CoinPoker responded by blocking the suspect’s account and reimbursing affected users over $100,000. GGPoker has since banned the use of third-party software and provided information about related wallets to law enforcement. ACR, meanwhile, stated it found no evidence of compromised hands and declined to offer compensation.
Why This Matters for the Industry
This incident highlights ongoing cybersecurity challenges for online poker operators, affiliates, and software suppliers. The attack demonstrates that even legitimate third-party tools can become vectors for sophisticated cheating schemes, underscoring the need for strict software vetting and robust monitoring. Operators may need to reconsider policies on third-party software integration, while affiliates and suppliers must increase vigilance around software security and update protocols to protect customers and their own reputations.
Key takeaways
- Hacker accessed player hole cards on major poker sites via malware in third-party tools.
- Malware targeted high-stakes players through compromised updates to Jurojin and IntuitiveTables.
- Losses estimated up to $4 million; some operators have reimbursed affected users.
- Incident raises concerns about software security and the use of third-party tools in online poker.